How this assessment was made. At the author's request, this assessment was produced by an AI-assisted review of the full, unredacted management chat and of public sources (company registers, court records, news reports, Reddit and forum posts, and Solar's statement of 30 November 2022). The review deliberately looked for evidence against the author as well as for him. It is not a legal finding and it is not neutral in origin: the author asked for it and published it. Please check the linked messages and sources yourself and reach your own view.
No court or authority has confirmed that Mike is Paul Vernon, or that Mike took the Altilly funds. Where this page says something is "likely" or "probable", that is the reviewer's judgement of the evidence, not an established fact. The author's own beliefs are labelled as his beliefs.
Scope and method
- The review read the whole exported chat, including the notes the author added in September 2026, and checked disputed items against the raw export and the attached images.
- Message numbers are written like #1232; each one links to the message. Items marked "(image)" come from photos or screenshots, not message text.
- Timestamps in the export are in UTC-8 (US Pacific). Add 9 hours for Central European Time.
- Some messages and images were redacted before publication to remove customer data, third-party personal data and credentials. See the Transparency page.
0. Corrections found while checking
These points were misread in earlier drafts or are easy to misread. They change the analysis.
- The "PAUL Vernon" Revolut envelope #3833 is Mike's card, not Nayiem's. The surrounding messages settle it:
- Nayiem tells Mike to order a card #3638. Mike asks "they send physical cards to china?" #3639, then reports "Sorry, our service is not offered in your country" #3646.
- Nayiem: "Send it to my address, I will send it to you then" #3647, and gives his own address #3648. Mike: "ok, done" #3653. Nayiem: "Mike is registered and ordered his card" #3693.
- Two days later a Revolut envelope arrives at that address, addressed to "PAUL Vernon" #3833 (image). Chuck: "card already?" #3834. Chuck's own card came separately in the US #3846.
- Mike later says "Here can take a few days to clear customs" #3837 and "i got my revolut card today" #3960. That fits the card being forwarded to China.
- So in February 2021 the person known as Mike held a Revolut card in the name "Paul Vernon". This is a record made at the time, not a later claim. The export shows no edit marker on #3833.
- #1033-#1034 are forwarded messages from Mike, not Chuck's own words. They were originally sent on 23 December 2020 at 22:11 (UTC-8): "I think the attack came in from maybe an insecure recue port at the host level" and "i've only found 3 machines affected". So Mike had reported an attack by the evening of 23 December. The next day he told the team to call it an "outage" #1057.
- "it's okay if I only get half back" #5203 is a hypothetical claimant speaking, not Nayiem. The full text reads: "So for example when a user just says: it's okay if I only get half back of what I've lost."
- #6813 is ambiguous. Nayiem says "I know you purposely strung it out to buy time. That's a good thing, because the next solution will be better", then "But I meant your time, yes" #6814. It still approves of a delay, but the full wording matters.
- Mike's house was not shown to be bought with money from after the hack. In May 2021 Mike moved into a "new house" #5094; the renovation and an indoor pool are documented #5106-#5125. At the same time he was selling another house, which he said had been bought about nine years earlier, and he found a buyer in September 2021 #4204, #5471, #6163-#6166, #7544. (An earlier draft of this review applied the "nine years" remark to the new house; in context it refers to the house being sold.) In September 2021 he said the furniture for the new house had been "sitting in a warehouse for a year" #7431. The author's 2026 notes, which present the house as "5 months after the hack" and say Mike "suddenly" had "10k out of nowhere" #7589-#7592, leave all this out. Nothing in the chat shows how the new house or the renovation was paid for.
1. What the chat establishes with high confidence
- "Deleted Account" is Mike (@MrMike_O), a different person from Nayiem.
- He answers when @MrMike_O is tagged or Mike is addressed by name, all through the chat (#790 → #792 → #794 "Well done Mike"; #1056 → #1059; #3162 → #3163; #4045 → #4048).
- He laughs at praise of "Mike" #304 and links github.com/mrmikeo #4380.
- A Fastmail ticket is addressed "Hi Michael" #3288, and he signs a whitepaper "Michael Osullivan @MrMikeO" #5529.
- He says he lives in China #1559, #2674, #3639. He received his own card abroad #3960.
- Nayiem was in Sweden at the time #5733-#5735. The claim that "Nayiem is Mike" is not supported by this record.
- Mike was the lead developer and technical operator from 2019: code deploys #22-#23, the admin panel #611, database payouts #416, #434, market structure #498 and payment settings #697.
- There was no audit and no real cold storage. Mike, 15 July 2019: "we are too small to worry about audits yet" #215 and "heck we are too small to even start moving to safe storage" #216. The public About page said the opposite #721 (image).
- The incident was on 23-25 December 2020, not 12 December. Mike's attack report dates from 23 December and was forwarded the next day #1033-#1034, a first, low estimate ("under 10k", "might be 15") came on 24 December #1056-#1059, and the servers were deleted on 25 December #1103, #1106.
- The loss was about USD 1 million.
- "around 31 bitcoins" #1600, and a USDT withdrawal wallet that still showed about $13k #1616-#1624.
- The team's own figure: "We lost 1mln" #1677. The BTC, ETH, DASH and DOGE wallets were "gone" #4094, #4095. About 137 assets were "saved" #1757.
- The author's own XQR (Qredit) coins held on Altilly were lost too: Chuck asks "is XQR safe?", Nayiem answers "Nope" / "All lost" #1731-#1734.
- The user database and the decryption settings were lost #1308, #1353, #5309. This is the root of the later problems with checking refund claims.
- Refunds of saved assets were actually sent in 2021, mostly by Mike.
- Refunds were incomplete and late. "thousands who were too late" #5052; first-round assets were still unpaid in July 2021 #6876. Chuck, September 2021: "Weve made alot of promises we are not keeping" #7421.
- Nayiem kept working closely with Mike until at least September 2021, on Qredit Motion, Altfenix, hosting and money #1885, #2128, #5658, #5728, #7428.
2. Who controlled funds, wallets, servers and keys
Mike, according to the chat (strong, consistent, and recorded at the time):
- The Cherry Servers account was set up with his email three years earlier #1504; "Mike uses cherry" #1483.
- Backups: "i should have had the backblaze api keys so you couldn't delete" #1271.
- The "safe" wallets: "I also had a VPS server there holding the 'safe' wallets" #1299. He held keys outside the database #1615, #1621.
- The encryption settings file was his, and he says he never kept a copy #1353, #3086.
- He handled Cloudflare DNS #1206, the database ("would have required me to do it in the db", #4344), Fastmail billing #3163, #3946, help-desk billing notices #5600, and the Twitter recovery email #4989.
- Keys he held later: TUSC #4878, HIVE #3917, the SLP deposit wallet #5186-#5190.
- He ran the sweeper by hand: "i just did it whenever funds were needed in wd wallet… entirely possible that i swept a large amount at some point and just don't remember" #6717-#6718.
- He moved funds on his own: PYRK to a "community fund wallet" #7096; XNC coins to a developer #1814, hours after Nayiem said not to transfer anything yet #1725.
Nayiem, according to the chat:
- At the time of the loss he said he had no access to the Cherry servers: "I never had access to those servers. Mike didn't allow me" #1492-#1493. He had to ask which host was used #1105 and whether keys existed #1285.
- He did have some access:
- The Hetzner account #6040 and the Cherry client relationship were in his name or Qredit's. Cherry's letter is addressed to Qredit and to Nayiem's Qredit email #4349 (image).
- Assessment: control of the systems that were wiped sat with Mike. Nayiem's access after the incident was real but limited. Nothing in the chat shows Nayiem had access to the lost BTC/ETH wallets or the safe-wallet server before the loss.
Companies (public registers and the author's account):
- The chat presents Altilly as a Hodler Enterprises company #702, #705, and in 2019 Nayiem wrote that it was "still incorporated in Hongkong" #759. In December 2020 Mike said a Hong Kong address came from "a company registration service i was going to use originally to form a company in hk. never did do that tho" #1778 (context #1776-#1779). These two statements conflict. No register we checked lists Altilly as a company.
- UK Companies House lists QREDIT LTD (no. 13077371), incorporated on 11 December 2020 at a London formation-agent address, with Nayiem Willems as sole director and the only person with significant control (75% or more). Mike does not appear on it, or on any register we found connected to Altilly. It never filed accounts and was struck off on 17 May 2022. The chat never mentions this company, and the export has no messages from 2 to 18 December 2020. Register: https://find-and-update.company-information.service.gov.uk/company/13077371
- The Revolut Business account was also Nayiem's; Mike was a cardholder on it. When Revolut asked Mike to verify his ID in March 2021, he put it off: "my passport is at the china visa office" #4414-#4416. Nayiem paid with his own card instead #4417. No later message shows Mike completing the check.
- The author says he was to receive ownership of the whole project once he had set up the company, which he did around December 2020. That is his account. The chat contains no message transferring ownership.
- The author says Qredit Ltd never traded because his XQR coins, which it depended on, were lost in the hack #1731-#1734. He believes Mike took the XQR along with the rest. That is a belief; the chat only shows that the XQR was lost.
- In December 2020 Nayiem wrote that "Willems Ventures" was registered at his home address, where his tourist resort was #1579, #1583. Per the author, Willems Ventures was the company for that resort and unrelated to Altilly. A UK company, Willems Ventures Ltd, was incorporated on the same day as Qredit Ltd, with a London registered office. The Revolut Business account the team used showed the name Willems Ventures #3686.
3. The December 2020 incident: timeline and conduct
| When (UTC-8) | What | Message |
|---|---|---|
| 23 Dec 22:11 | Mike to Chuck (forwarded the next day): attack via "insecure recue port", "3 machines affected" | #1033-#1034 |
| 24 Dec 07:12 | Nayiem: "Mike, can you give me more details about the hack that happened?" | #1031 |
| 24 Dec 17:12 | "Is it really under 10k Mike?" / "might be 15" / "wont know for sure until i get everything moved" | #1056-#1060 |
| 24 Dec 17:12 | Mike: "Just tell them that we are still investigating the outage, and we have full control of our systems." | #1057 |
| 24 Dec 17:21 | Chuck: the status page shows missing assets. Mike: "yea, ill fix that soon" | #1077-#1079 |
| 25 Dec 14:12-14:41 | Mike: the host "deleted all the servers", backups gone. The host's first email said cancelled for non-payment; Mike: "that's a lie". Then: "a change i made didn't allow them to access - so i guess they got pissed off and just deleted everything" | #1103-#1132 |
| 25 Dec 15:44 | Nayiem: "it will backfire if we don't tell the truth." | #1163 |
| 25 Dec 16:29 | Nayiem wants to say "hackers were unable to access funds". Mike: "we don't know this" | #1180-#1183 |
| 25 Dec 17:18 | Public notice: suspicious activity, a new system user, lost "the domain, several wallets and the whole codebase", "not sure yet if funds are lost" | #1167, #1232 |
| 26 Dec 01:48-02:15 | Mike: the attacker came in through an old email on the account, "[email protected]"; "history on that domain probably has my name" | #1289, #1326-#1328 |
| 26 Dec 16:12-16:33 | Mike: DIME funds went to a wallet that is "ours"; Backblaze cannot recover; Cherry says the deletion came from the inactive email over Tor | #1497-#1513 |
| 27 Dec 00:01 | Nayiem, on Cherry's reply that "all of your servers data was cleaned" #1564: "Don't share this with anyone yet until I have my stuff ready." | #1566 |
| 27 Dec 03:09 | Mike: "around 31 bitcoins"; "i have no access to that wallet to even check" | #1600-#1601 |
Mike's conduct:
- Every technical fact came from him alone, and his explanations changed: a rescue port, then Cherry's "non-payment", then "they got pissed off", then the old email, then Tor.
- He recommended calling it an "outage" and changing the status page.
- He could not name the address of the BTC safe wallet he says he kept #1615, #2121, and suggested "just say we are investigating" #2124.
- He disabled command history and kept a full-access backup key in a shared server guide #2587. (That Backblaze key was revoked long ago; the key in the guide no longer works.)
- He talked about quitting crypto within a day #1332.
- Each of these fits negligence, and each also fits insider action. None of them proves insider action.
Nayiem's conduct:
- He pushed for disclosure #1163, stayed on as public admin #1245, argued against going silent #1249, and pressed for the BTC to be traced #1511, #1599, #2113.
- He also accepted the "outage" wording without objecting #1057-#1075 and helped word the softened notice ("Like this maybe?" #1072). He was ready to publish an unverified reassurance #1180. He asked to delay telling users that the data could not be recovered #1566.
- The technical claims in the public notice ("new system user", "above OS level") appear to come from Mike's reports #1033; he described the same rescue-mode method again the next day #1510. The claim that the domain was lost was wrong: Mike was repointing its DNS at the time #1206.
Chuck handled messaging and moderation and was alert to liability ("they will be expecting you to pay up", #1190). He flagged the MOON and DIME movements himself #1278, #1494. The chat shows no sign that he controlled any wallet.
4. Mike's identity, and the question of Paul Vernon
Established from the chat: "Deleted Account" = Mike = @MrMike_O = GitHub "mrmikeo", who presented himself as Michael O'Sullivan (§1). Public records add that a "Michael Osullivan" was listed as Altilly's developer on Bitcointalk in December 2018, and that UK Companies House lists a director registered as Michael O'Sullivan for Xeggex Software Services Ltd (Companies House). The register does not verify identities. The author believes "Michael O'Sullivan" is an alias Mike used. That name may belong to a real, separate person whose name was used. Nothing here accuses any such person.
Evidence that the person behind "Mike" used the name Paul Vernon:
- 26 December 2020 #1326-#1328: Mike himself names the old hosting-account email "[email protected]" and says "history on that domain probably has my name". This was written before anyone had a reason to point at him.
- February 2021 #3646-#3693, #3833 (image): Mike's Revolut card, sent to Nayiem's address at Mike's request, is addressed to "PAUL Vernon" (see §0).
- Public records (not court findings): The DOJ alleges that Paul Vernon of Cryptsy moved to China around November 2015. The domain satotechltd.com is linked to Vernon by an anonymous 2016 forum post and by a WHOIS record the author posted in 2026 #7577 (image).
- #4529: on Cryptsy's stolen coins, Mike writes "we had noticed they hadn't moved years ago". This is ambiguous.
- Mike says he joined the army in 1991 #5456. That is broadly consistent with Vernon's age (born about 1973). One published source puts Vernon's enlistment in 1994, a small unverified difference.
A further name match involves a private person. It is withheld here and not relied on.
What this does and does not show:
- Items 1 and 2 were recorded at the time and do not depend on Nayiem's later account. In the reviewer's judgement they make it highly likely that Mike used the name Paul Vernon, and probable that he is the Cryptsy founder of that name.
- Reading "satotechlt" as a typo for "satotechltd" is the author's 2026 interpretation #7595.
- No court or authority has confirmed this. A card name reflects what the account holder registered, and it is not known how strictly Revolut checked team members' names in 2021. When Revolut did ask Mike to verify his ID in March 2021, he deferred it #4415, and the chat does not show him completing it.
- Public record: Paul Vernon was indicted in Florida (filed 2019, made public January 2022) over Cryptsy. He has not been convicted, and the charges are allegations. No filing in that case mentions Altilly.
- The chat does not show Mike staging the loss. If Mike is Vernon, an insider theory becomes more plausible. It would still not be proven.
- This also cuts against Nayiem. He held an envelope reading "PAUL Vernon" in February 2021, and he says he "always knew that Mike never used his real name" #7595. He says he searched the name and found only a blues musician #7585, #7595. That is plausible but cannot be checked. It weakens any claim that he had no clue about Mike's identity. It supports his claim that he could not prove who Mike was at the time.
5. Refund handling
What was done:
- A claim form was opened #2029 with a repay mailbox #2025-#2028. The deadline was cut to 9 January 2021 #2443 (image), and a quieter late form followed #2447, #3357.
- Claims were checked against deposit-confirmation emails and capped at the amount on the form #2146, #4665, #4828, #4870.
- Saved assets were paid:
- Saved wallets were often short: Betller "thats all we had" #4686, Blocknet #7450, HONK only 5.25B recovered #6750, MRX wallets at 0 #4849.
- By September 2021 Chuck had built sheets for non-saved assets and a BTC claim page with "800+ users… over 1600 entries" #7426, #7517-#7519. The chat shows no payment for non-saved assets.
The separate list #4029-#4033: Nayiem told Chuck to refund a "really pushy person" "not by email and remove all traces" #4029. The list in question was the banking partner's 139-country high-risk list, not a sanctions list, though Chuck said he got "a sense this list covers all sanctions of any type" #4023, #4027, #4028. Nayiem explained that one long-standing user with proof of saved assets was on that list (he called it "the sanctioned list"); he put him on a "separated list" to "pay out eventually in the end" and deleted the messages #4032. The author says the users on that separate list were paid. The chat does not show the payment. The instruction to "remove all traces" and the off-record handling of a user on the bank's list remain fair grounds for criticism.
Amounts in the chat: a loss of about $1M #1677; "1 million usd can be done" #1626; "we can not mine for 200k usd" #5184. Nothing in the chat supports "$900K paid from my own pocket". The author says the 2025 phrase "$2.4M saved assets" was wrong: $2.4M was the team's final total of all claims, saved and non-saved assets together, not the saved assets alone and not the loss. That claims sheet is not in the chat; the chat shows the valuation being set up #2534, #2553 and the non-saved-asset and conversion sheets being built #7426. Claims can exceed the loss because they include saved assets that still existed and were valued at a later date. Until the sheet is published, $2.4M is the author's figure.
- In January 2021 Nayiem wrote that he had "no money at all" #2805, and in May 2021 "zero cash" #5602.
- He paid some running costs, such as topping up the company card #4387 and paying the help-desk and email bills with his own card #4417-#4420.
- Personal repayments, if they happened, would be after October 2021 and outside this record. They are the author's claim until documents are published.
- The author says he stopped paying refunds around 2022/2023, with only a handful after that, and estimates the claims still unpaid at around $50,000–60,000. That estimate cannot be checked: the database was lost and many of the chains no longer exist. See Refunds.
How it went, weighed both ways:
- For good faith: a structured process #3965, with a transaction ID per username #3993; checking developer refunds on-chain #3224; keeping the saved-asset lists public at Chuck's insistence #7159; and confirmations from third parties.
- Against:
- Delay as a tactic: "I can drag it out forever" / "Go for it." #5017-#5020; a refund-token plan followed the next day #5201-#5203, but Altfenix never launched; also #6811-#6813, #5962, #6027.
- The lowest valuation described as "most beneficial for us" #6842, though the author says the aim was to keep a one-day altcoin price spike around the hack from setting the value.
- Dated repayment promises removed #3418-#3421; a public repayment promise removed #1911-#1918.
- Loose checks: "anything between 50-200 usd I don't check at all" #3564, with only each coin's total claims checked against its wallet balance #3558; no payout ledger #3575.
- Insiders exempted from proof #3953.
- The off-record payout above #4029-#4032.
- Refund support paused for product work #6035.
- Refunds for non-saved assets tied to future ventures and IOU tokens #5201-#5203, #5878-#5883, #6806.
6. The author's 2025 statement, claim by claim
| Claim (2025 statement or follow-up) | Verdict | Evidence |
|---|---|---|
| Nayiem is not Mike | Supported | §1; #3646-#3693 |
| Mike was the developer who controlled operations, wallets and servers | Supported | §2 |
| Nayiem had no access to Cherry | Supported for Cherry; other access existed | #1492-#1493, #1105; compare #2569, #7119 |
| The collapse began on 12 Dec 2020; $10k/$15k on 13 Dec | Contradicted: 23-25 Dec | #1033, #1056-#1059, #1103 |
| Collapse came "twelve days after forming the company" | Supported by the register: Qredit Ltd was incorporated on 11 Dec 2020, and the incident began on 23 Dec, twelve days later. The "12 December" date in the same statement looks like a mix-up with the incorporation date. The chat itself never mentions the company | Companies House 13077371; #1033 |
| Registered "Altilly" in the UK | Not supported: the UK company was Qredit Ltd, not Altilly. In 2019 Nayiem said Altilly was incorporated in Hong Kong #759; Mike said the HK company was never formed #1778 | #759, #1778 |
| Official story was a hosting breach / "database corruption" | Partly: servers deleted and data wiped, not "corruption" | #1103, #1564, #2493 |
| Mike was "fixing" the database and never did | Partly: the database was said to be lost; he chased a possibly unwiped disk; no follow-up | #1353, #2491-#2511 |
| Only low-cap coins were saved because migration started with them | Partly: recent bitcoin-clone listings were on the new host | #1297-#1301, #1370 |
| $900K refunds paid from his own income | Not supported by the chat: later payments would fall outside this record | #2805, #5602 |
| $2.4M "saved assets" (the author now says: total of all claims, saved and non-saved) | Not checkable: the final claims sheet is not in the chat; the chat's loss figure is about $1M | #1677, #2534, #7426 |
| Paid refunds from his own funds over 2-3 years | Not supported by the chat: he was broke in 2021, and Mike sent refunds in kind | #2805, #5602, #4836 |
| Mike showed off his house, pool and office while the team struggled | Partly: May 2021 videos show a new house, still under renovation, with an indoor pool. Mike was also selling another house, which he said had been bought about nine years earlier. Nothing links either house to Altilly funds, and the 2025 claim of a villa bought with stolen funds is not supported | #5094, #5106-#5125, #5471, #6163-#6166, #7430-#7431, #7544 |
| The Altilly "hack" was a cover / inside job | Not established: circumstantial only, and at odds with Nayiem's own conduct and Altilly's public line in 2020-21 | §3, #1256, #2128 |
| Mike offered money after the hack | Supported ("that 10k", "send a little extra"); the stated purpose was licence costs | #5728-#5738 |
| Mike = Paul Vernon | Partly supported: strong name evidence; legal identity unconfirmed | §4 |
| Karl = Mike; GitHub; Xeggex | Not addressed by the chat (after it ends) | - |
| Mike asked him to be CEO in 2018 | Not addressed, and inconsistent with his other statements: the chat starts in 2019; Nayiem acts as CEO; Hodler Enterprises named as owner. His personal website says "I acquired Altilly in 2018 and invested $175,000 personally", and Altilly's 2020 notice said it "was acquired in 2019" | #702, #705 |
| A "two-way dialogue" was opened with the US Marshals | Partly supported, by the author's account: a two-way dialogue was opened and tip reference 777-W77728 issued, with no response beyond that; the 2025 wording implied more | - |
| Chosen as a scapegoat because he was the public face | Partly: he was the public face and his address was public #1579; team faces were removed from websites #1264-#1265 | #1579, #1264 |
| Some stolen funds went to the EXMO/Livecoin hackers' wallets | Not supported by the chat: only "state sponsored" speculation | #1054 |
| MRX/FARM taken over-the-counter by Mike | Not supported: MRX wallets at 0; no OTC evidence | #4849 |
| Vernon "never criminally charged" | Contradicted by the public record (indictment made public January 2022) | - |
| (Conduct in the 2025 write-up) It named a private person linked to Mike's postal address, linked a property listing, and said Mike's details would be shared "if there was a 100% guarantee that people would visit his location" | Documented in the write-up itself. The author now says this was wrong. This site withholds those details | - |
7. Reddit and public allegations
| Allegation | Status against the chat |
|---|---|
| Nayiem is Mike, or Mike was invented | Contradicted (§1, §4) |
| Nayiem and his wife stole the funds / exit scam | Not supported: no message shows Nayiem moving customer funds, and he appears broke. It cannot be ruled out, because the record is one chat, curated by him |
| Negligence (no 2FA on the host, no backups) | Supported: the old hosting login had no 2FA, and the backups could be deleted along with the servers #215-#216, #1271, #1299, #1504 |
| 14-day claim window, short deadline | Supported #2443; softened by the quiet late form #2447, #3357 |
| Deposit-email proof used to keep payouts low | Partly supported: a stated anti-fraud reason #5867 alongside minimising language #6842, #5017-#5020 |
| Only partial refunds; some never paid (Banano, TUSC, etc.) | Supported #5052, #6876, #7377, #7421 |
| Payment priority by country | Partly: country screening (Chuck: "declined refunds due to sanctioned countries") #4005 and the banking partner's 139-country high-risk list #4028; Nigeria deliberately not marked #4034 |
| Admins deleted critics and class-action talk | Supported #2679-#2683, #3929-#3934 |
| Deposits and withdrawals failing days before | Not addressed directly; the 38-pending-withdrawal event is from 2019 #790 |
| Nayiem knew about Mike and stayed silent (re Xeggex) | Partly admitted, outside the chat. In the 2025 statement a Discord message of 30 November 2022, 00:17, reads "We are not going to say anything if you can return the funds in 24hrs" (image). It concerned the 1,878,477 SXP fraudulently swapped from Solar, as described in Solar's statement of 30 November 2022; by the author's account Mike repaid the full 1,878,477 SXP in 12 payments between 1 December 2022 and 19 March 2024. He admits he put recovering that money ahead of warning Xeggex users. See §9 on what could be checked |
| A CEO without server access is implausible | Addressed: the chat shows it at the time #1492-#1493, #2572, #6557 |
| Screenshots not from Nayiem's device | Not addressed |
| Karl = Nayiem; Dokdo/Xeggex links | Not addressed by the chat (2022 onwards) |
8. How Nayiem comes across
- Business-focused, and a delegator. He set direction and fees and left technical matters to Mike ("I don't know. Mike knows", #3841). He did not insist on audits or proper custody, although he did raise BitGo and Chainalysis #961-#964 and, later, manual cold-wallet withdrawals #5666.
- During the crisis he pushed for disclosure and stayed reachable #1163, #1245, #1249. He was supportive of colleagues ("It's not your fault", #1256). He was distressed and frightened by threats #2366-#2471: "I don't know what i will do to myself if it ever happens again" #5361. He was short of money.
- Also:
- impulsive and sometimes careless: the unverified "funds safe" line #1180; blaming Mike over DNS and then correcting himself #7119-#7123; posting his own card details in the group #4417;
- focused on PR and at times opaque #2968, #2973, #3147, #4029-#4032, #7179;
- dismissive or mocking towards some claimants: "What an idiot" #2158; "I like it when Altilly users are saying that they are going to sue me" #6386; "10% approval… more than enough" #5059;
- quick to move on to new ventures while refunds were pending #2304, #5236-#5257, #6035.
- Fair summary: the chat reads like an overstretched operator who trusted and depended on a technical partner, and who then handled the fallout with a mix of real effort, self-protection and messaging that users would reasonably call evasive. It does not read like the planner of a theft, but that impression has limits (§9).
9. Limits of this evidence
- One source, curated by an interested party. Nayiem became owner of the group on 28 September 2026 #7576-#7578, removed messages to protect customer and third-party data #7598, and added notes in 2026 written with hindsight #7576-#7598.
- Who could delete what. Before 28 September 2026 Nayiem had no admin rights in the group #7576-#7578; like any member, he could delete his own messages. Chuck created and owned the group until then, and Mike could delete his own messages until his account was deleted. At least one missing message number, #7582, comes after Nayiem became owner. The export does not show who deleted what, or when.
- Some gaps (missing message numbers, so they cannot be linked) fall at sensitive points: around the 24 December wording (#1030, #1055, #1058, #1061-#1064, #1066-#1070); around the [email protected] email (#1323, #1325, #1327, #1329-#1331, #1333); and #3095-#3101 with several more up to #3116, #3402, and #7499, #7502-#7503 and #7506-#7507. Customer data does not obviously explain these gaps.
- Much happened outside this chat: Mike's direct messages and calls #2716-#2718, #6561, Discord, the public groups, the help desk, forms and spreadsheets.
- Mike's account is deleted and he cannot respond here. Several key items are images.
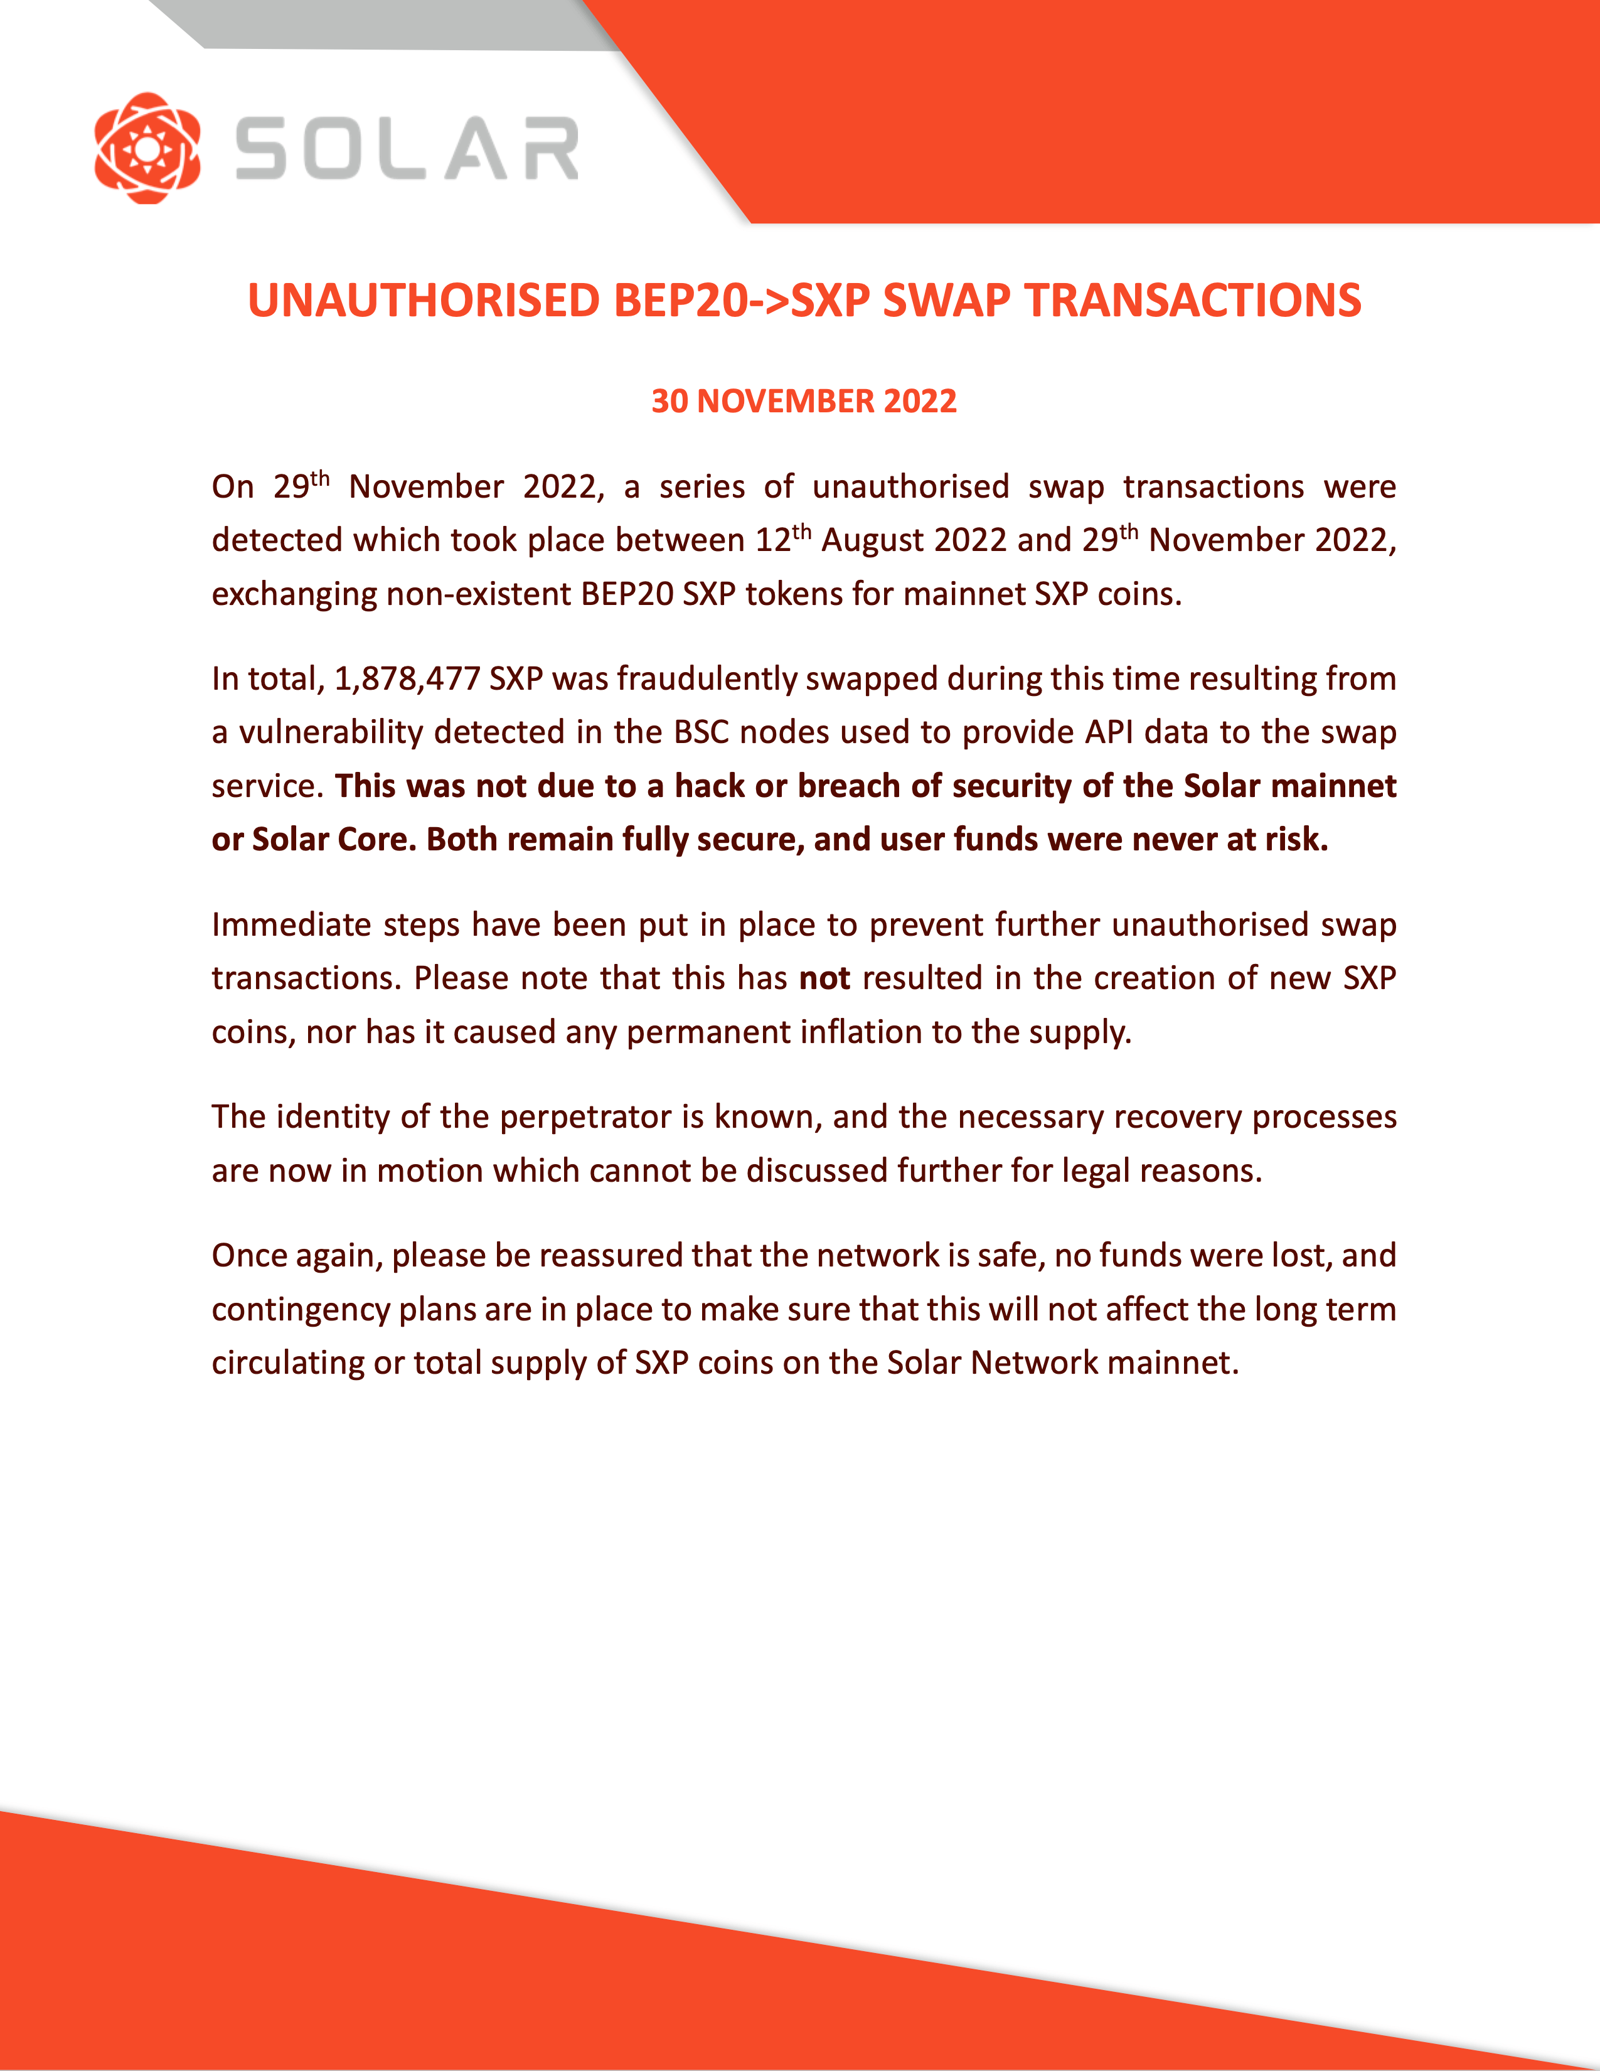
- The November 2022 Solar incident: what is documented and what rests on the author. Solar's statement of 30 November 2022, posted in the Solar validator group on Discord and titled "UNAUTHORISED BEP20->SXP SWAP TRANSACTIONS", says that on 29 November 2022 unauthorised swaps were detected which took place between 12 August and 29 November 2022, exchanging non-existent BEP20 SXP tokens for mainnet SXP coins; that "In total, 1,878,477 SXP was fraudulently swapped" through a vulnerability in the BSC nodes that provided API data to the swap service; that this was not a hack of the Solar mainnet or Solar Core, "user funds were never at risk" and no new SXP was created; and that "The identity of the perpetrator is known, and the necessary recovery processes are now in motion which cannot be discussed further for legal reasons." The statement does not name Mike. Mike's identity as the perpetrator comes from the author's Discord screenshots in his February 2025 write-up: on 29 November 2022 at 22:45 the author wrote "Why did you do it Mike?", and at 05:43 on 30 November MikeO replied "sorry man. ya i fucked up… original plan was to earn some money from trading… liquidated out of my positions on the ftx crash… only thing that is possible is to return it as i can get it." These screenshots are the author's evidence and were not independently verified here. The repayment rests on the author's account: he says Mike repaid the full 1,878,477 SXP in 12 payments between 1 December 2022 and 19 March 2024, back to the Solar swap wallet involved in the theft. His repayment ledger gives transaction IDs for the final five payments, which can be checked on the Solar blockchain; the first seven have no published IDs, and a transaction alone does not show who sent it.
- Law enforcement. The author says he reported to the FBI and the US Marshals Service in early 2025, that the Marshals opened a two-way dialogue and issued tip reference 777-W77728, and that there was no response beyond that. No authority has made any public statement about Altilly, Xeggex or Mike.
- Cannot be proven from this record: who deleted the servers; where the 31 BTC went; whether Mike acted deliberately; whether any funds reached Nayiem; the $900K in personal repayments.
What would strengthen the author's case:
- a full export from another member (such as Chuck), with a checksum, to compare the gaps;
- Revolut records for the "Paul Vernon" team member, and the original envelope photo with its metadata;
- Cherry Servers records showing the account owner, logins, and who registered the [email protected] email;
- on-chain tracing of the Altilly BTC/ETH hot and safe wallets and of the DIME destination wallet #1497;
- bank and exchange records of personal refund payments, with a ledger;
- for the Solar incident: transaction IDs for the loss and for the seven earlier repayments (the receiving wallet and the final five repayments are listed in the author's ledger);
- any acknowledgement from law enforcement.
What would weaken it: another member's export showing incriminating deleted content; on-chain links from Altilly outflows to addresses Nayiem controls; or evidence that he held the Cherry credentials or safe-wallet keys before 25 December 2020.
10. Overall conclusion
- High confidence: Nayiem is not Mike. Mike, not Nayiem, ran and held the keys to the wiped servers and the lost wallets. The loss was about $1M, in late December 2020. Nayiem appeared short of money through 2021.
- Moderate to high confidence: the chat contains no evidence that Nayiem stole Altilly funds. His conduct at the time (pushing for disclosure, chasing the BTC, staying reachable, and being short of money through 2021) fits someone who did not.
- Highly likely in the reviewer's judgement, but not legally established: Mike used the name "Paul Vernon" #1326-#1328, #3833 with #3646-#3653. Probable, but unconfirmed, that he is the indicted Cryptsy founder.
- Not established: that Mike orchestrated the "hack". There is suspicious circumstantial material: sole control, changing explanations, a BTC wallet he could not recall, the "outage" wording, the status-page fix, missing records, and the possible Vernon identity. There is also material that fits an outside attack: Cherry confirms an earlier intrusion #4353 (image), Mike reported a Tor source, and EXMO and Livecoin were hacked in the same days. Nayiem trusted Mike through 2021, so his inside-job theory is a later reinterpretation, not a view he held at the time. It remains his belief.
- Fair criticisms of Nayiem that the evidence supports: poor governance as CEO; accepting a partner under an assumed name; refund management that was opaque, sometimes stalled, and aimed at limiting liability; refunds that were never completed; an off-record payout with an instruction to "remove all traces"; several factual errors in his 2025 statement (the 12 December date, "never criminally charged", figures the chat does not support, wording that made the "two-way dialogue" with the Marshals sound like more than it was); publishing a private person's details and inviting people to visit Mike's location in 2025; and, by his own account, offering in 2022 to stay silent if Mike returned the Solar funds, while Xeggex users went unwarned.
- Fair headline: not shown to have stolen; shown to have failed on governance and on refund transparency; his central claim about Mike's identity is better supported than his critics allow; his central "inside job" claim is plausible but unproven.